SQL注入行为实时在线智能检测技术研究
2020-12-21李铭邢光升王芝辉王晓东
李铭 邢光升 王芝辉 王晓东
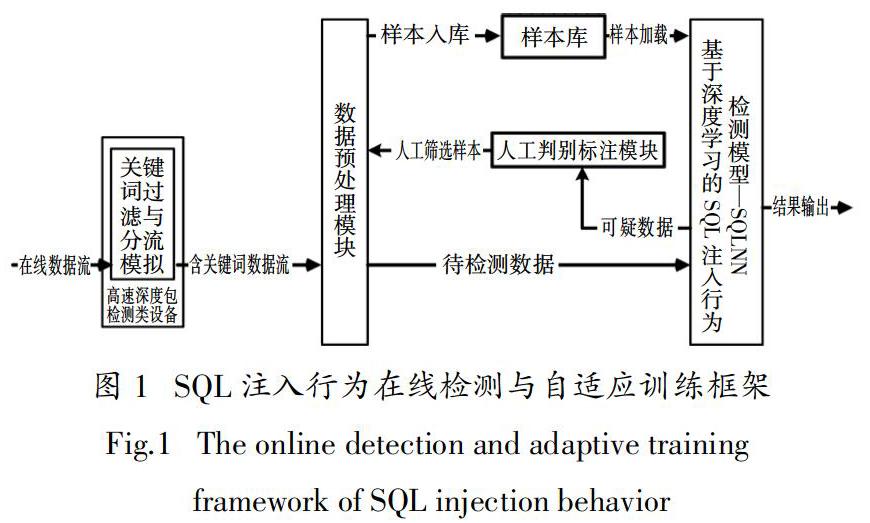
摘 要:为了解决传统手段在实时高速网络流量环境下SQL注入行为检测准确度和效率之间无法达到较好平衡的问题,提出一种基于深度学习模型的SQL注入行为实时在线检测的方法,构建了以卷积神经网络为基础并引入快速傅里叶变换层的复合检测网络模型SQLNN,并以此模型为基础提出SQL注入行为在线检测与自适应训练框架. 该框架对于SQL注入语句的检测正确率达到了99.98%,每秒可完成对一万条左右含有SQL语句的数据包的检测,满足了SQL注入攻击的实时在线检测对检测准确度和效率的要求.
关键词:SQL注入;实时检测;卷积神经网络;快速傅里叶变换
中图分类号:TP391 文献标志码:A 文章编号:1674—2974(2020)08—0031—11
Abstract:In order to solve the problem that traditional methods cannot achieve a good balance between the accuracy and efficiency of SQL injection behavior detection in the real-time high-speed network traffic environment, this paper proposes a method for real-time detection method of SQL injection behavior based on deep learning construction model, and constructs a detection network model called SQLNN based on Convolutional Neural Networks (CNN) and introduces a fast Fourier transform layer. Based on this model, an online detection and adaptive training framework for SQL injection behavior is proposed. For our detection framework, the detection accuracy of the SQL injection statements reaches 99.98%, and it can detect about 10 000 packets containing SQL statements per second. Therefore, it can satisfy the requirements of real-time online detection of SQL injection attacks for detection accuracy and efficiency.
Key words:SQL injection;real-time detection;Convolutional Neural Networks(CNN);Fast Fourier Transformation(FFT)
随着互联网技术的快速发展,各种网络攻击手段层出不穷,SQL注入攻击作为网络安全领域中最常见的攻击方式已有十多年的历史,根据开放 Web 应用安全项目组织(Open Web Application Security Project, OWASP)正式發布的十大 Web 应用安全风险报告,SQL注入已经成为对Web业务系统威胁最严重的行为之一.攻击者常常利用网络应用漏洞,渗透并进一步获取后台服务器控制权,然后执行篡改页面、窃取数据等恶意操作. SQL注入方式主要是通过构建恶意的SQL语法组合作为参数输入Web应用程序,应用程序执行SQL语句时会同步执行恶意操作,进而发生SQL注入攻击. 如果应用程序代码执行过程中将含有攻击者输入的恶意字符串进行存储或传递,也会导致SQL注入的发生. SQL注入有多种方式,按照构造……