基于贝叶斯分类算法的网络入侵行为检测方法
2020-11-13何新洲
何新洲
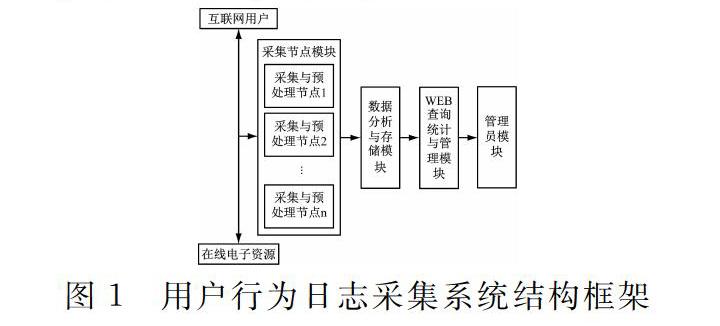
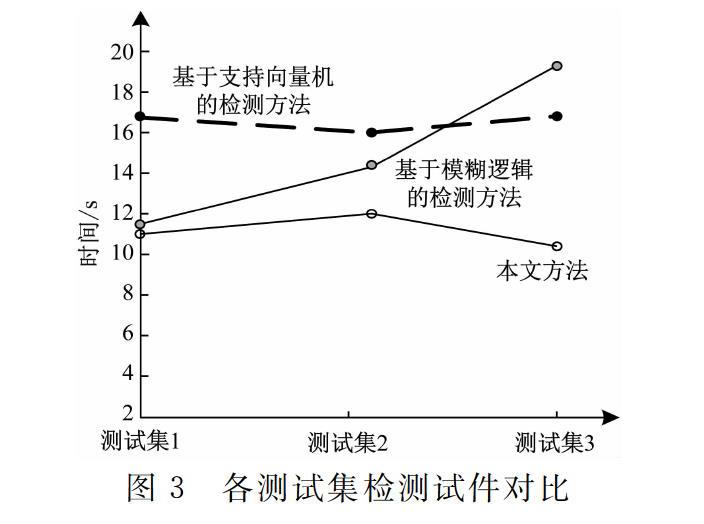
摘要:传统的网络入侵行为检测方法检测时间长、检测率低,导致网络安全受到严重威胁,因此基于贝叶斯分类算法对网络入侵行为检测方法进行研究。首先设计用户行为日志采集系统,通过采集节点模块、数据分析与存储模块对用户行为日志数据进行采集,其次通过消除冗余数据、数据规范化等环节预处理采集到的数据。针对预处理后的数据,构建基于朴素贝叶斯分类的网络入侵行为检测模型,基于不同的属性集构建非网络入侵与网络入侵分类规则,实现网络入侵行为检测。实验结果显示该方法检测结果准确度在97%以上,检测过程花费时间与对比方法相比降低4s以上。
关键词:贝叶斯分类;网络入侵;行为检测;行为日志;属性;分类规则;卡方检验法
中图分类号:TP393
文献标志码:A
NetworkIntrusionDetectionMethodBasedonBayesianClassificationAlgorithm
HEXinzhou
(DataandInformationSchool,ChangjiangPolytechnic,Wuhan430074,China)
Abstract:Thetraditionalnetworkintrusiondetectionmethodhasalongdetectiontimeandlowdetectionrate,whichleadstoaseriousthreattothenetworksecurity.ThispaperstudiesthenetworkintrusiondetectionmethodbasedonBayesianclassificationalgorithm.Firstly,theuserbehaviorlogcollectionsystemisdesigned,itcollectstheuserbehaviorlogdatathroughthecollectionnodemodule,dataanalysisandstoragemodule,andthenpreprocessesthecollecteddatabyeliminatingredundantdataanddatanormalization.Accordingtothepreprocesseddata,thenetworkintrusiondetectionmodelbasedonnaiveBayesianclassificationisconstructed,andthenonnetworkintrusionandnetworkintrusionclassificationrulesbasedondifferentattributesetsareconstructedtorealizethenetworkintrusiondetection.Theexperimentalresultsshowthattheaccuracyofthemethodismorethan97%,andthedetectionprocesstakesmorethan4slesstimethanthecomparisonmethod.
Keywords:Bayesianclassification;networkintrusion;behaviordetection;behaviorlog;attributes;classificationrules;Chisquaretest
0引言
隨着互联网技术在人们日常生活中的普遍使用,具有复杂性和连通性的开放系统逐渐替代原有的独立系统[1],随着而来的不仅是互联网强大的使用功能,还有网络安全与计算机安全问题。在此条件下,高效的网络入侵行为检测方法研究对于网络安全具有重要意义,是网络信息安全建设的关键环节[2]。
检测互联网上无授权计算机资源使用情况的行为即网络入侵行为检测[3]。目前已有很多学者网络入侵行为检测方法进行相关研究。刘强、蔡志平等学者针对入侵检测框架、特征自动生成、安全检测理论及方法等问题进行研究,梳理出网络安全检测算法和框架、并总结了网络安全检测与控制技术发展趋势。……