软件定义边界下的可信动态访问控制模型研究
2020-10-27王骏彪
王骏彪
【摘 要】
针对传统访问控制模型引发的数据泄露和安全问题,结合企业不断提升的数据泄漏防范要求,提出软件定义边界下的可信動态访问控制模型,利用数据的语义信息、数据来源信息、数据使用模式计算数据访问的可信度,以此来强化动态访问策略,在评估数据的可信度上用户干预性最小,根据访问数据集实时情况所引起的可信度变化来调整访问控制策略。实验结果表明,该模型能够以较少的开销增强对多源数据集的访问控制,解决了当前软件定义边界下云平台中访问控制模型安全性不足的问题。
【关键词】可信度;动态;访问控制策略;数据语义信息
[Abstract]
In view of the data leakage and security problems caused by the traditional access control model and the continuous requirements of data leakage prevention from the enterprises, this paper proposes a trusted dynamic access control model under the software-defined boundary, which uses the semantic information, data source information and data usage mode to calculate the credibility of data access, so as to strengthen the dynamic access strategy and minimize the user intervention in evaluating the data credibility. Furthermore, the access control strategy is adjusted according to the credibility change caused by the real-time situation of the access data set. The experimental results show that the proposed model can enhance the access control of multi-source data sets with less overhead, and solve the problem of insufficient security of access control model in cloud platform under the current software-defined boundary.
[Key words]credibility; dynamic; access control policy; data semantic information
0 引言
随着通信技术和信息化技术的快速发展,企业从各种来源获取的数据会引发安全漏洞和数据安全问题。在企业使用的各种数据中,非结构化数据是企业数据库的重要组成部分,这源于非结构化数据内容丰富,呈现多样化。如此信息丰富的数据一旦泄露,将会对公司造成损失。基于传统文件级别的访问控制技术,数据的可靠性只能从人工经验或者从提供的信息中进行识别,不能满足现代数据量激增的访问控制要求,因此,构建一个能够根据数据可信度的动态访问控制模型很有必要。本文提出一种软件定义边界下的可信动态访问控制模型。
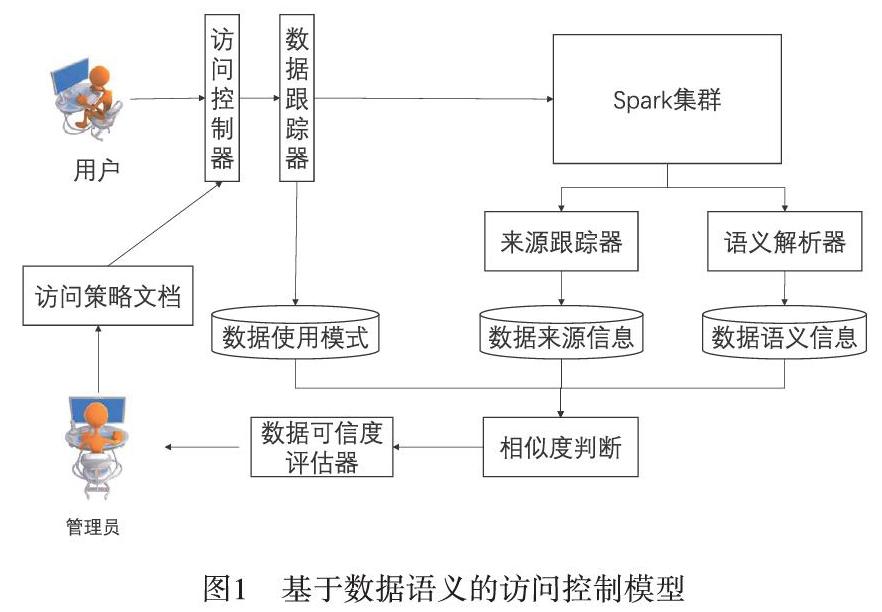
软件定义边界是基于用户上下文而不是凭证来授权企业资产访问,通过以用户为中心的动态访问控制来验证连接用户的身份,采用访问控制模型来解决大数据环境下授权的即时性和访问的动态性。……