基于Linux的ARP检测与防御系统
2018-06-29陈军孙义博岳婷
陈军 孙义博 岳婷
摘 要:ARP协议,即地址解析协议,由于协议存在的漏洞导致ARP欺骗几乎无法避免。为探讨如何解决这一问题,通过理论研究和实证,论文从主动和被动两个模块提出了ARP检测与防御的方法。主要思路是利用基于Linux的开源路由器系统OpenWRT定制路由器,对网络流量进行监测,一旦主机网络流量达到一定阈值时,通过对其进行检查来判断源主机是否遭受ARP欺骗,以维护局域网的安全运行。
关键词:ARP检测与防御;主动检测;被动检测与防御;Netfilter;OpenWRT
中图分类号:TP393 文献标识码:A
ARP detection and defense system based on Linux
Abstract: ARP, the Address resolution protocol, owing to the loopholes of the protocol, leads to ARP spoofing almost impossible to avoid. In order to explore how to solve this problem, through theoretical research and empirical analysis, this paper puts forward ARP detection and defense methods from two modules of active and passive. The main idea is to use the open source router system customized OpenWRT router based on Linux, monitoring the network traffic.Once the host network traffic reaches a certain threshold,,we will examine and determine whether the host is deceived, to maintain the safe operation of LAN.
Key words: ARP detection and defense; active detection; passive detection and defense; netfilter; openWRT
1 引言
在局域网中,每台计算机都拥有两个地址,即IP地址和MAC地址。实际应用时,若想根据一台机器(主机或路由器)的IP地址找出该台机器相应的硬件地址(MAC地址),则需要使用地址解析协议ARP。对于每台装有TCP/IP协议的计算机,均存在一个ARP缓存表,表里存放着对应的IP地址和MAC地址。同时,计算机中的ARP缓存表是动态变化的,会根据所收到的ARP应答不断地进行更新,以保存最近的IP地址和MAC地址。然而,对于大多数操作系统,它不会去判断自己是否发送了ARP请求,而会根据所有接收到的ARP应答对ARP缓存进行更新,这便对计算机造成了潜在的安全威胁。攻击者利用这一漏洞,并伪造IP和MAC进行ARP欺骗,对攻击目标(受害方)实施恶意攻击,截获通信过程传输的信息。因此,为了更好地保障网络的安全,需要在攻击者对源主机成功实施ARP欺骗之前,检测到ARP欺骗并采取防御措施。
2 ARP欺骗
2.1 ARP欺骗原理
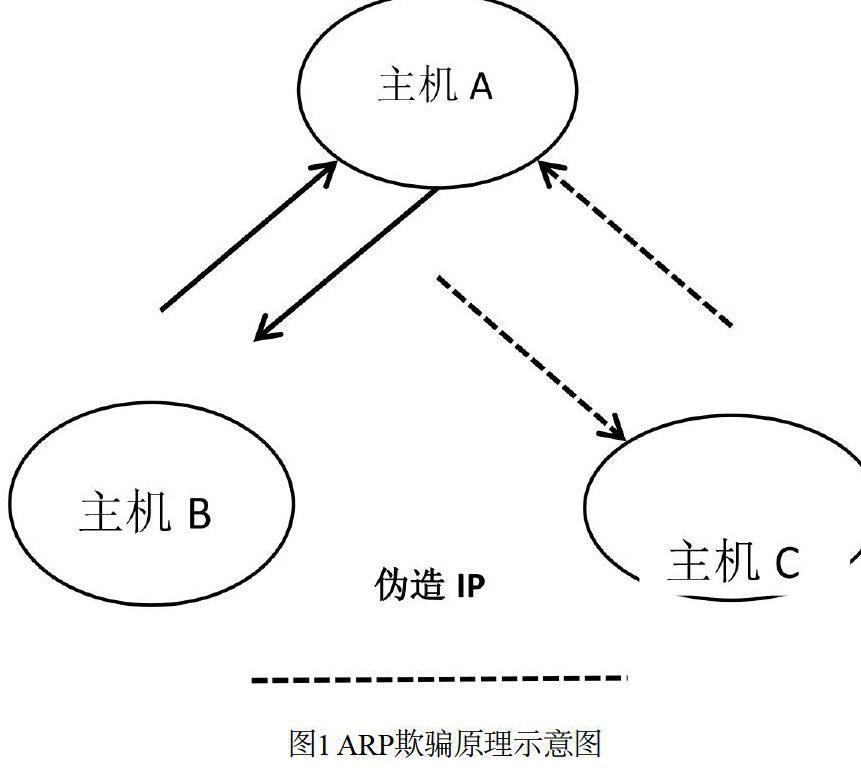
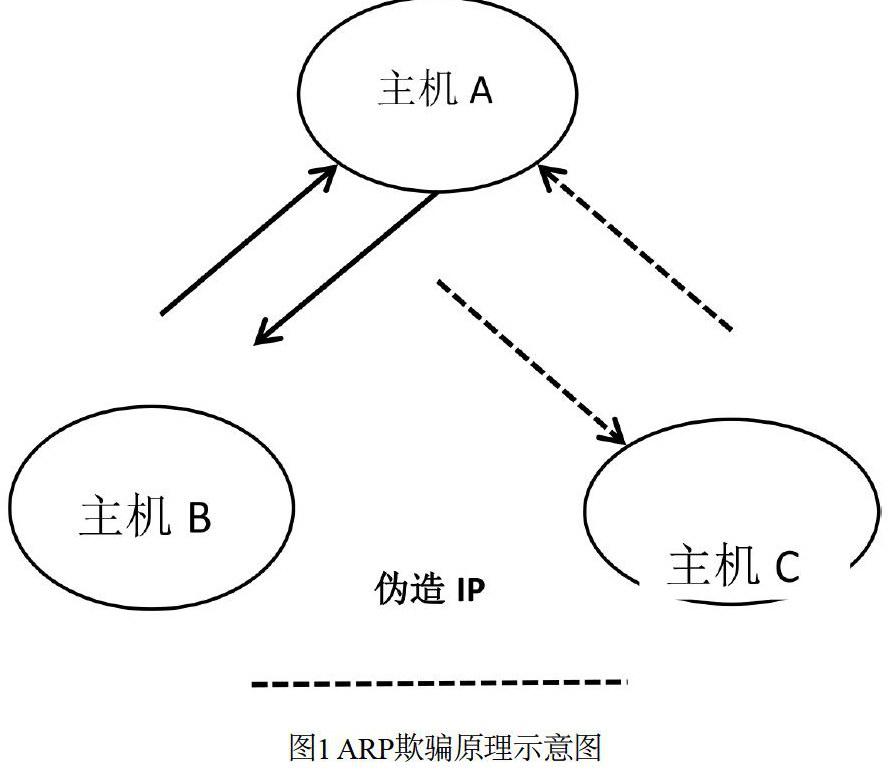
数据包在以太网中传输,寻址依据是计算机的物理地址(MAC地址)。……