基于代理的Web应用安全管控系统设计与实现
2017-09-30杨永群章翔凌黄勤龙肖志恒
杨永群++章翔凌++黄勤龙++肖志恒
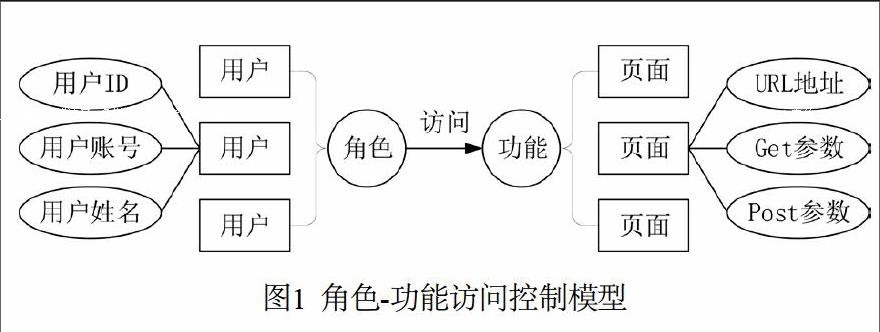
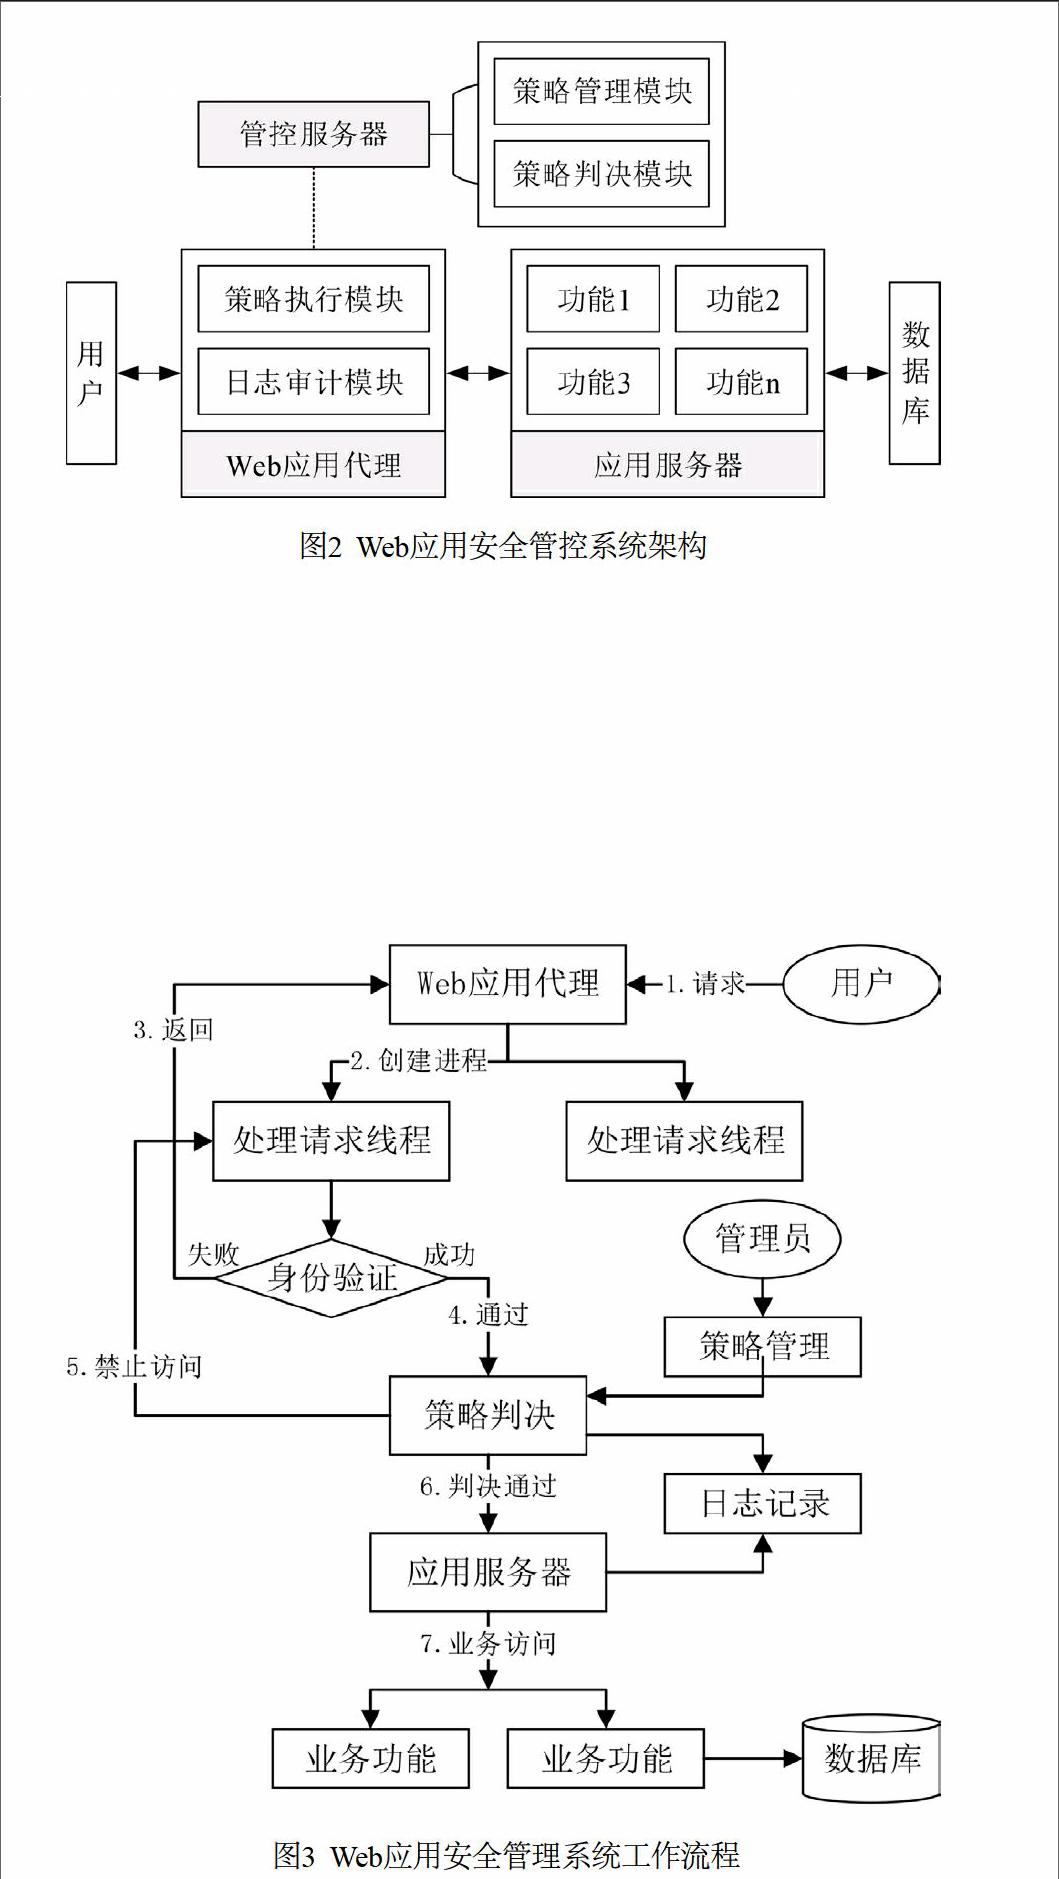
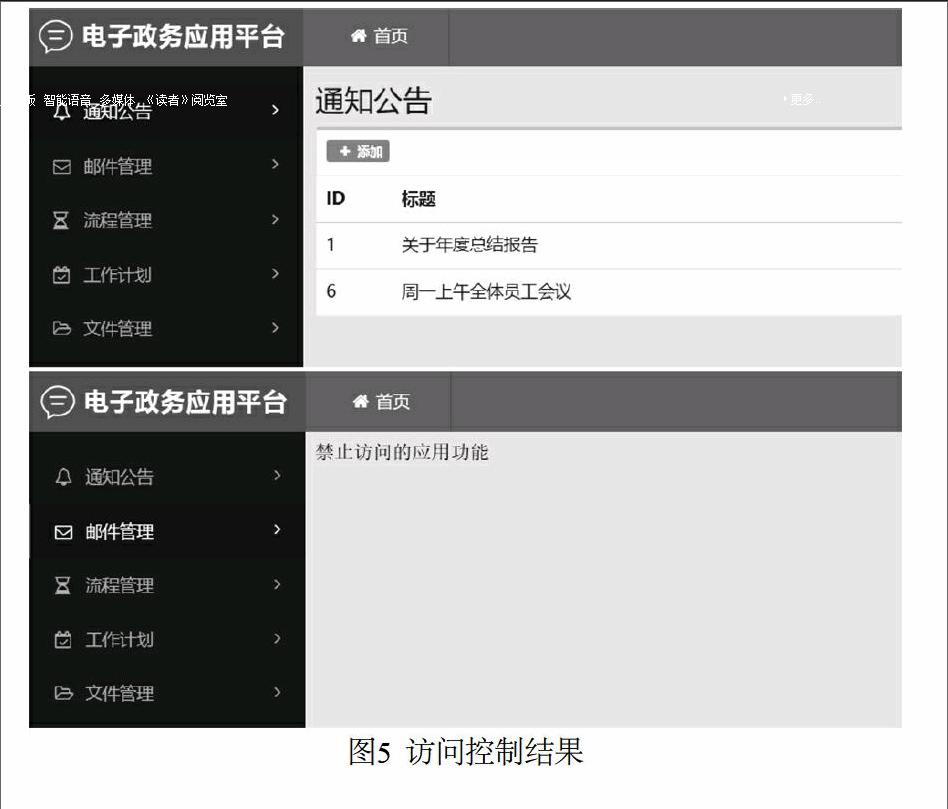
摘 要:针对现有Web应用访问控制的不足,在基于角色的访问控制模型基础上提出一种基于代理的Web应用安全管控方法。首先,根据用户访问控制的需求,以页面为单位划分Web应用的业务功能,构建角色-功能的访问控制模型,实现用户对Web应用功能的细粒度访问控制;其次,对Web应用安全管控系统的整体架构及各功能模块进行设计,通过代理的方式在Web应用前端部署管控系统,控制用户对Web应用系统的所有访问行为,阻止未授权用户的Web应用访问,并最大程度减少对现有Web应用系统的改动;最后,对系统进行了实现,结果表明系统能有效地实现电子政务等Web应用的安全管控。
关键词:Web应用;应用代理;安全管控;访问控制
Abstract: Aiming at the shortcomings of access control models in current web systems, a web application security control framework based on proxy is proposed on the basic of role-based access control. Firstly, according to the requirements of user access control, the business functions of web application are divided by page, and a role-function access control model is built, which achieves fine-grained access control of web application functions. Secondly, we design the architecture of a web application security control system and its functional module, in which the control proxy is deployed in the front-end of web application, and it makes the access behavior of user to the web application functions is under control and the unauthorized access to the web application is blocked. In this way, it can minimize the changes to existing web applications. Finally, we implement the designed system and the result shows that the system can achieve effective security control of electronic government and other web applications.
Key words: web application; application proxy; security control; access control
1 引言
从普通用户的角度来看Web系统,其被看成一系列页面的合集,这一系列页面在向用户提供其需要的数据的同时也向用户提供了各类操作。Web页面中的数据是通过网页中HTML标签展示给用户,而页面的操作指页面向用户提供的如新增、删除、修改等各种交互行为。用户在使用Web浏览器观览页面时,页面会通过显式或隐式的方法告知用户完成某工作或任务的操作步骤,因此,用户对Web系统的操作皆通过对页面的访问来实现。在Web应用系统中,由于不同的Web系统涉及到不同的业务,而各种业务具有多样性,所以Web页面的组织形式也灵活多样[1]。
访问控制是保证Web应用系统完整性、机密性、可用性的一种主要技术手段,它通过限制对某些控制功能的使用来确保Web应用资源在合法的范围内使用,保证用户在授权范围内访问Web应用资源。……
